KVM Lab — Isolated Bastion, Ansible & Teleport
A personal virtualisation lab reproducing a realistic enterprise setup: KVM/Libvirt virtual machines, automated deployment with Ansible, strict network isolation through a bastion, centralised and audited SSH access with Teleport, and traced outbound internet through a proxy.
- Context
- Personal lab
- Field
- Networks & systems · Security
- Tools & technologies
01
Context & Goal
Goal: build, on a personal Debian machine, a full virtualisation lab (KVM/Libvirt) reproducing a realistic enterprise topology — an automation controller, a bastion, and three role-specific servers (web, application, database) — then automate their deployment and secure access the way a real infrastructure would.
02
Architecture & Network Isolation
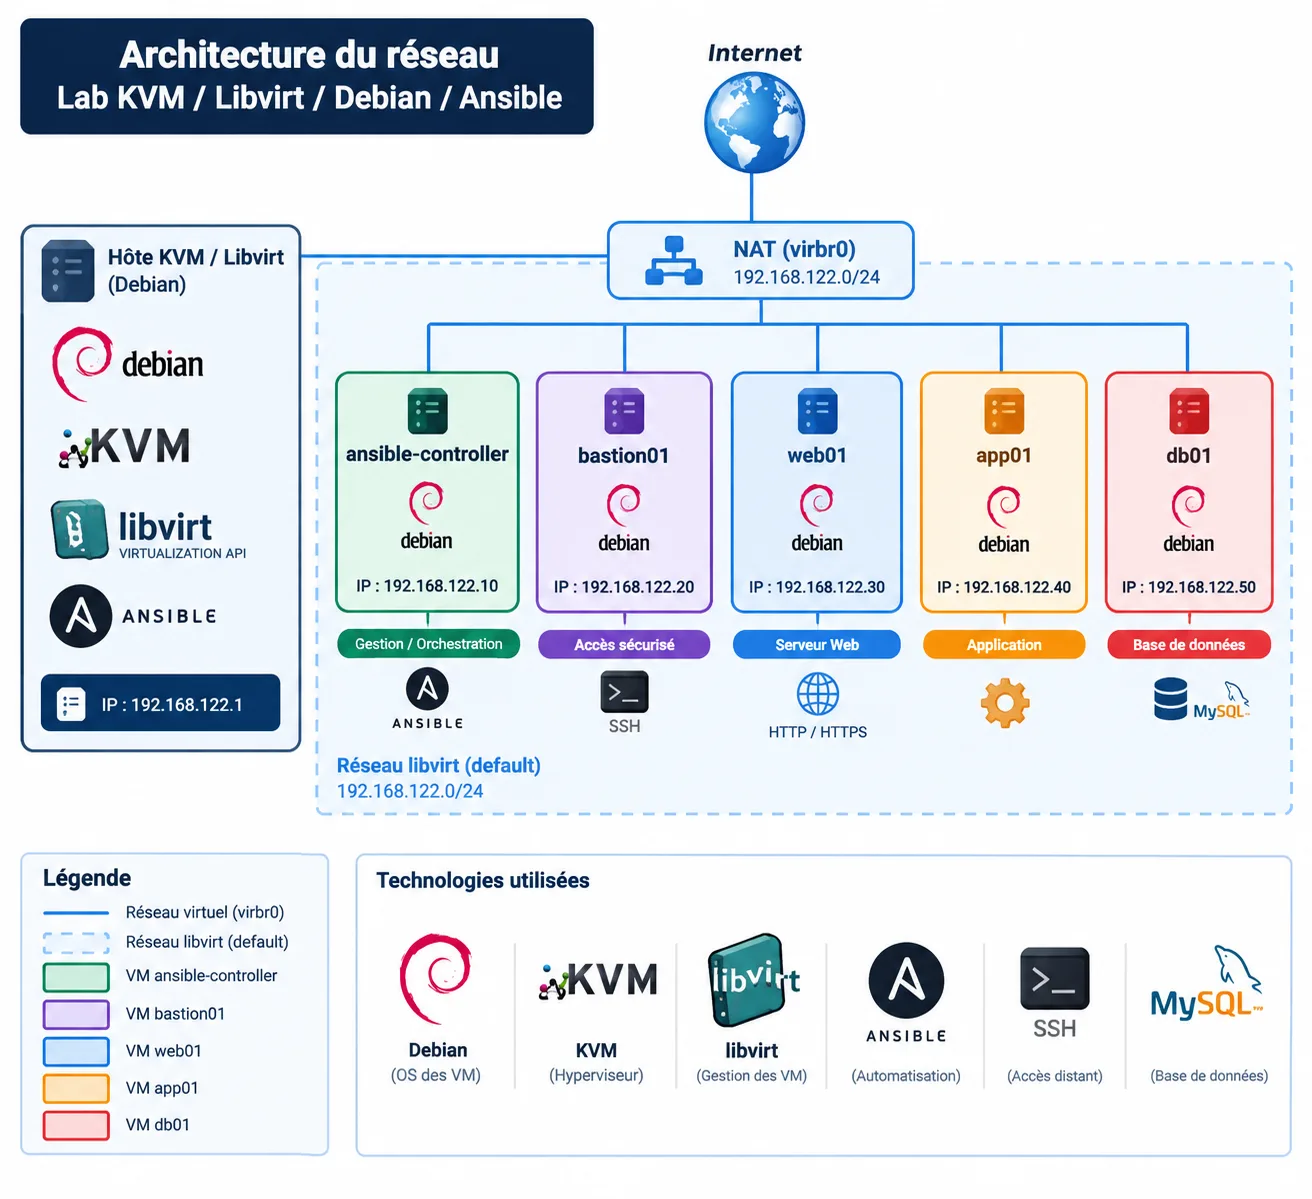
Five Debian VMs on a KVM/Libvirt host: ansible-controller (orchestration), bastion01 (secure access), web01 (nginx), app01 (Docker) and db01 (MariaDB). The bastion is the only dual-homed machine: on one side the default network (NAT, 192.168.122.0/24), on the other an isolated network (10.10.10.0/24) with no NAT and no host-side address — no route exists between the host and the isolated VMs. No firewall is used: the topology itself forces every access through the bastion.
03
Automated Deployment with Ansible
The controller drives the three role servers via Ansible playbooks, reaching the isolated network through an SSH ProxyJump via the bastion. Each service is installed, configured and enabled idempotently.
- Inventory using
ProxyJumpto reach web/app/db with no direct route from the controller - Dedicated playbooks: Nginx (web01), Docker (app01), MariaDB (db01)
- On Debian 13, the Docker GPG key is stored in
/etc/apt/keyrings/and referenced viasigned-by(apt-keyno longer exists)
04
Centralised & Audited Access — Teleport
Teleport runs as a cluster on the bastion (auth, proxy, audit), accessed through a named user with MFA (OTP) rather than raw SSH access. The isolated VMs (web/app/db) join the cluster via a reverse tunnel to the bastion without needing to be directly reachable — each agent initiates the outbound connection itself.
- Authentication
- Named user + MFA, no more shared SSH accounts
- Recorded Sessions
- Every
tsh sshconnection is logged and replayable - Token-Based Enrollment
- Dedicated Ansible playbook, short-lived token + CA pin
05
Controlled Outbound Internet — Tinyproxy
Since the isolated VMs have no outbound route, an HTTP proxy (Tinyproxy) is installed on the bastion: it only listens on the isolated leg and relays to the internet through the host’s NAT leg. Every apt request from the isolated VMs thus goes through a single, traced and auditable point, instead of an invisible transparent NAT.
06
Skills Acquired
- KVM/Libvirt Virtualisation
- Creating, managing and networking VMs with virsh/virt-install
- Ansible Automation
- Idempotent playbooks, ProxyJump-based inventory
- Network Isolation
- Designing a routeless topology, bastion as the single entry point
- Secure Access & Audit
- Teleport (MFA, reverse tunnels, logged sessions)